Pay or Consent Model: Why Paying with Personal Data is Under Legal Fire | GDPR Compliance
Pay or Consent: The Legal Battleground Around Paying with Personal Data The digital landscape has introduced a new dilemma affecting…
Read more →
How Is the GDPR Doing Worldwide?
The General Data Protection Regulation (GDPR) came into force on May 25, 2018 within the European Union. More than seven years later, it’s…
Read more →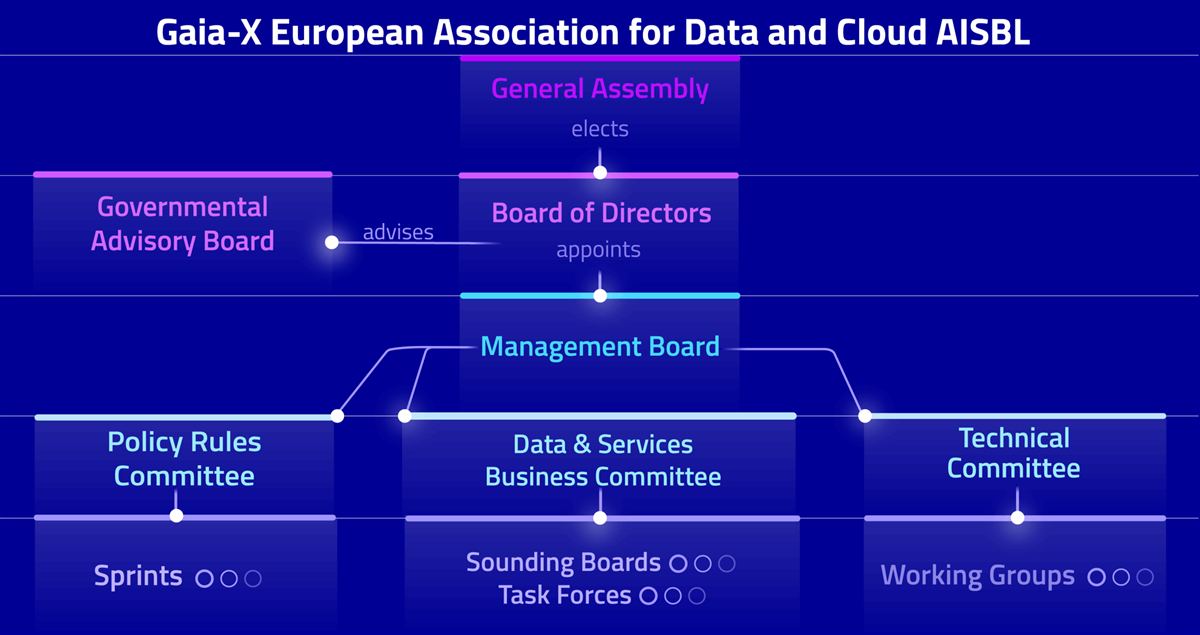
GAIA-X: The Logical Choice for Maximum GDPR Assurance at Lower Cost
Introduction: What Is GAIA-X? GAIA-X is a European collaboration initiative that helps companies and institutions exchange data safely,…
Read more →
What is a regulation? Allowed and Prohibited Procedures, and Practical Implementation
1. What Is a Regulation and How Does the GDPR Work? 1.1 The Legal Nature of a Regulation A regulation is a binding legal rule that applies…
Read more →
EU–US Data Privacy Framework: Why Now Is the Time to Consider European Alternatives
1. Data protection is not optional In the European Union, privacy is a fundamental right. The GDPR sets strict conditions for processing…
Read more →
Marketing and Personal Data Under the GDPR: What’s Still Allowed?
Organizations are using more personal data than ever to improve their marketing. From CRM systems and newsletter platforms to tracking user…
Read more →
Managing Personal Data? Here’s How to Monitor Retention, Minimization, and Data Quality
As an organization, you collect personal data for all kinds of purposes, customer service, invoicing, marketing, support. But how do you…
Read more →
Want to Keep Contacting Customers? Here’s How to Collect Personal Data Responsibly and Long-Term
As an organization, you want to stay in touch with your customers, whether it’s for email campaigns, offers, loyalty programs, or…
Read more →
Deleting Personal Data Under GDPR: Don’t Wait for a Request
Many organizations think they only need to delete data when someone explicitly asks for it. But under the GDPR, deleting personal data…
Read more →
Cybersecurity Checklists: Practical Tool or False Sense of Security?
Checklists are a popular method to manage cybersecurity risks. But how effective are they really? Too often, they create a false sense of…
Read more →
What Is NIS2 and Why This European Directive Matters for Your Cybersecurity
Cyberattacks and digital incidents are becoming more frequent, with increasingly serious consequences. To help organizations prepare, the…
Read more →
Why the 10 NIS2 Security Measures Are Crucial for Cybersecurity and Privacy
Cyberattacks are making headlines more than ever, with serious consequences for both business operations and the protection of personal…
Read more →
Why NIS2 Matters for SMEs, Even If You’re Not Directly Covered
What Is NIS2 and How Is It Different from the GDPR? The NIS2 Directive (Network and Information Security) is the successor to the original…
Read more →
The 6 Biggest GDPR Risks for Your Organization, and Why Structural Compliance Is Essential
Nearly seven years after the introduction of the General Data Protection Regulation (GDPR), more and more organizations recognize the…
Read more →
GDPR in Practice: Why Municipalities Need More Than Policy on Paper
Gaining Control Over GDPR Compliance: Why Municipalities Need a Practical Solution The Case: Structural Challenges in Local Government…
Read more →
Schrödinger’s Personal Data: Does It Exist or Not?
The Data of Schrödinger’s Cat In day-to-day practice, the question “Is this personal data?” often seems easy to answer: a name, email…
Read more →
ISO Certified? Here’s Why That Doesn’t Mean You’re GDPR Compliant
Many organizations proudly hold ISO certifications like ISO 27001 or ISO 9001. While these certifications are valuable for demonstrating…
Read more →From reading to fixing.
RealCob checks every GDPR and NIS2 obligation and makes it demonstrable. Try it free for 30 days or book a 20-minute demo.