“I don’t have to be an expert to be compliant. In one afternoon I had an overview and a plan of action.”
Sound familiar?
Nobody gets excited about the GDPR. But it is not going away.
Four things we hear at every organisation:
“It’s mandatory, but it earns us nothing.”
Every euro and every hour spent on compliance is not spent on your customers. So it keeps sliding, quarter after quarter.
“A DPO or consultancy costs thousands a month.”
External advisers write reports and walk away. A year later, you get to start all over again.
“When there’s a data breach, I’m the one explaining.”
To the regulator, to your customers, to the press. Without a file you are empty-handed, and the damage to your name is permanent.
“Why does this law even exist?”
To keep data exchange — and with it national and international trade — possible. Organisations that never sort it out eventually get passed over as trading partners.
One platform
Everything the law requires, in one program.
RealCob checks what is missing and generates what you need. Facing an audit or a data breach? Then you simply show that it is all in order.
- ✓ Processing register
- ✓ Data breach protocol
- ✓ DPIA assessment and policy documents
- ✓ Audit-ready reports for regulators
Built-in AI agent
No lawyer? No problem.
The AI agent is right there at every question. Everyone in your organisation can work with it, from the boardroom to the shop floor.
- ✓ Explains every question in plain language, no legal jargon
- ✓ Tells you which supporting evidence to upload
- ✓ Gives you a ready-made format when a document is still missing
- ✓ Answers follow-up questions, like asking a colleague
How RealCob works
What takes a DPO months, you will have mapped in an afternoon.
Scan your organisation (± 3 hours)
Answer simple questions per department. No prior knowledge needed: the AI agent explains everything along the way.
Generate your documents
Data breach protocol, processing register, policies: RealCob structures and pre-fills them. Already have your own protocol? Then you simply use that.
Stay compliant
Automatic alerts on regulatory changes and risks. Checking your status once a month is enough.
What does NOT doing it cost?
A DPO costs €3,500 to €5,000 a month. RealCob a fraction of that.
Have a DPO? Mandatory in your sector.
Your DPO distributes the work across departments with RealCob: everyone answers only their own questions, the software compares the answers and flags what deviates. Full oversight on one dashboard, without months of walking the floors.
No DPO obligation? One coordinator is enough.
No need to hire anyone or bring in an external agency. One colleague manages RealCob alongside their day job. And when an audit or data breach comes, your file demonstrably holds up.
€42,000 – €60,000 per year → from €855 per year
Pricing
No surprises. This is what it costs.
Basic
€855 / year
- ✓ Full GDPR & NIS2 check
- ✓ All documents and reports
- ✓ Certificate included
Business
€2,250 / year
- ✓ Everything in Basic
- ✓ Multiple roles with their own login (DPO, IT, legal)
- ✓ Answers cross-checked between roles for consistency
- ✓ Real-time reporting + AO/IB module
Custom
On request
- ✓ Sector-specific customisation
- ✓ For large organisations and consultants
- ✓ ISO checks available
Prices per year · See all pricing →
Why RealCob?
The 14 advantages at a glance
Most tools record what you have documented. RealCob checks whether your organisation actually works that way. Almost no competitor does that.
- 01 Everyone handles only their own part: each employee sees only the questions that match their job
- 02 Nothing gets forgotten: data is recorded by the people who actually work with it
- 03 Procedures stay correct: continuous monitoring of your internal controls
- 04 One dashboard, full oversight: instantly see what is missing or deviating
- 05 Stay ahead of data breaches: work instructions prevent mistakes before they happen
- 06 Errors visible immediately, fixed immediately
- 07 Demonstrable towards regulators and auditors: proof of what was checked, when and by whom
- 08 No more annual project: GDPR becomes part of normal operations
- 09 Not dependent on one person: if someone leaves, compliance carries on
- 10 Contradictions flagged automatically: answers, registers and documents are cross-checked
- 11 Only relevant questions: smart question trees skip what does not apply
- 12 Every department works the same way: standard departments with pre-selected questions
- 13 Documents always up to date: changed policies automatically join the next cycle
- 14 Every cycle better and faster: you only re-process what changed
Choose your role
Tailored to your sector
Your DPO is mandatory, but does not have to do everything by hand.
RealCob maps every department and aligns with NEN 7510. Patient data protected, without straining your systems.
One coordinator, every location in view.
Student data protected and your DPO obligation demonstrably fulfilled, for schools and universities alike.
Accountable to the council and the regulator? One dashboard.
Audit-ready reports per department, continuous monitoring, and public trust that starts with privacy.
Also for SMEs, corporates, privacy consultants and suppliers to NIS2 entities
Rendement Boeken
DE AVG
CODE
De privacywetgeving
ontcijferd
Drs. M. Hiele
en Mr. J. Peters
The makers
Built by the people who wrote the book on it.
RealCob was built by Martin Hiele and John Peters, authors of De AVG Code (the Dutch GDPR handbook, available from Rendement) and immersed in privacy law practice for years. That knowledge is baked into every question, every document and every piece of advice in the software.
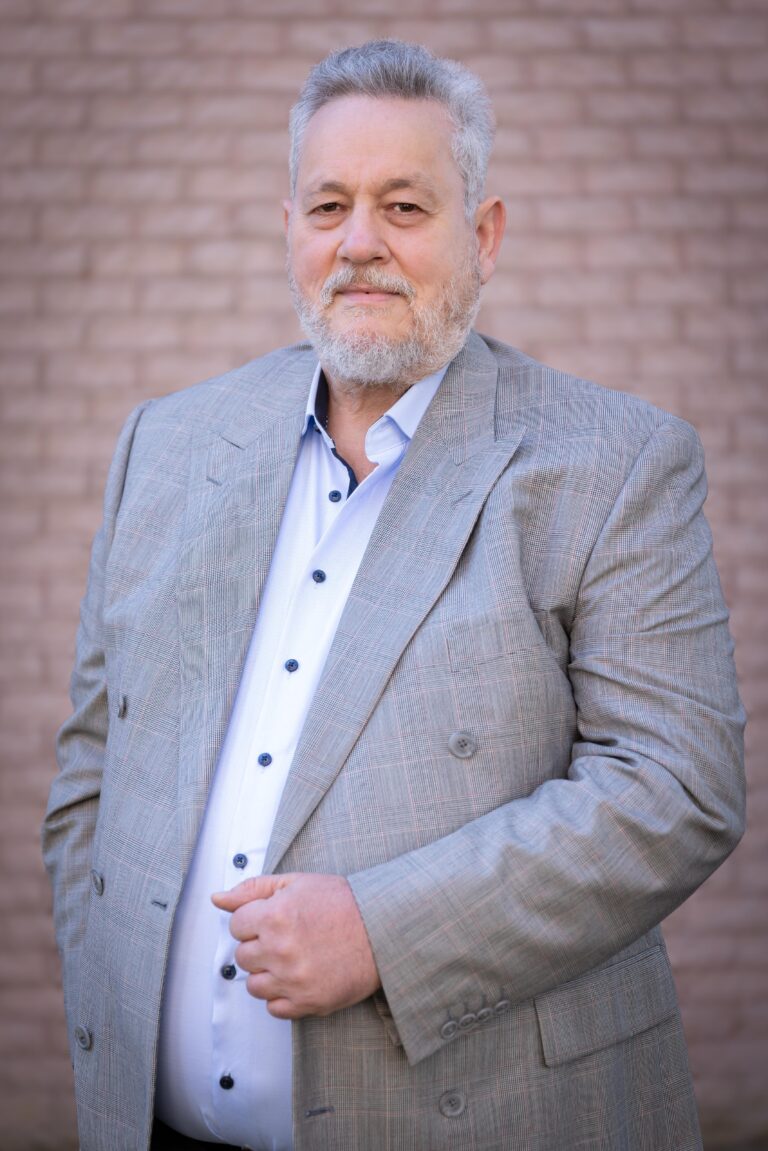 GDPR/NIS2 Compliance Architect
Designed RealCob’s control methodology and has guided organisations through the GDPR for years.
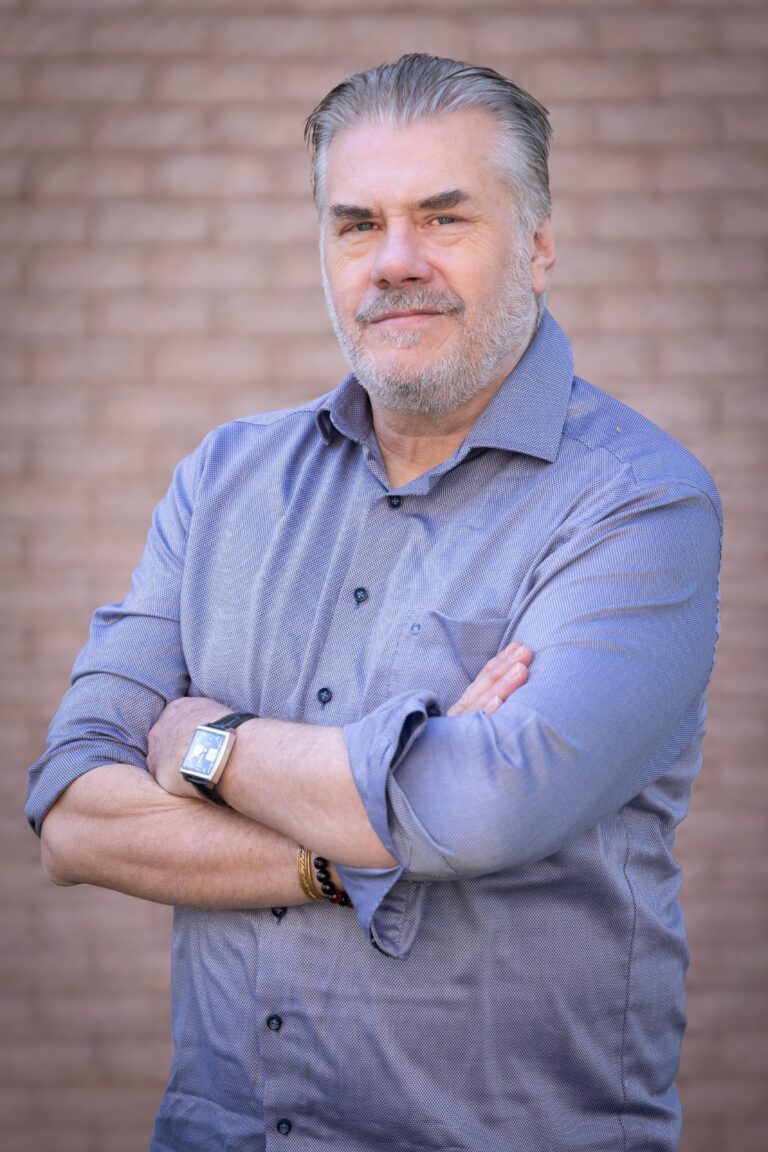 GDPR/NIS2 Expert & Lawyer
Lawyer. Ensures that every question, document and piece of advice in RealCob is legally sound and workable.
What our customers say
Positive experiences from our users
“As an SME, I finally have peace of mind. I am happy if I can get my daily work done, let alone have time to delve into GDPR or NIS2. RealCob was a breath of fresh air. The software took me step by step, gave clear advice and kept everything neatly. No complicated legal nonsense, just clear and practical.”
W.A.E. van den Heuvel · owner, Raad op Maat B.V.
“As a business service provider I want to offer certainty to customers. In our industry, trust is key. With RealCob, we can demonstrate that we are serious about securing data and complying with the law. This not only helps us internally, but also strengthens our position with customers.”
Bert Boer · owner, Diis
“In the business world, reliability is everything — RealCob delivers. Our clients expect us to handle their data securely. RealCob enables us to do so in a demonstrable way. The software seamlessly integrates with our processes, and thanks to its reporting functionality, we can substantiate everything during audits.”
Bas Hudepohl · Commercial Director, QSXL
“I don’t have to be an expert to be compliant. As the owner of an SME, I am not a lawyer, but I do have to comply with the GDPR and NIS2. RealCob makes it understandable and manageable. In one afternoon I had an overview and a plan of action.”
Yassine al Bargui · DPO, Fusernet Services B.V.
“Everything I need is in it. I am self-employed and do not have time to study legislation. With RealCob I do not have to. The tool shows step by step what I need to do and when. Everything is in understandable language, and I find that so refreshing.”
Gert Mossink · owner, 24/7 Work Company B.V.
“This software helps you get your GDPR compliance in order in a clear and user-friendly way. By answering step-by-step questions, you gain a clear understanding of what is needed to comply. The biggest advantage is that once you have completed the entire process, you can be confident that everything is properly arranged.”
Jessica Bitter · Marketing & Communications, Van Leeuwen
“I have regained control over my business risks. Compliance used to be something I didn’t like to think about — too vague, too big. Now I check our status in RealCob every month, get targeted advice and have an overview of all risks.”
Cris Scherrenberg · controller, Scherrenberg B.V.
Frequently asked questions
What you probably still want to know
Is RealCob enough to comply with both GDPR and NIS2?
Yes. Every obligation from both laws is checked, and you can demonstrate which checks were performed, when, by whom and with what outcome. Exactly what regulators, auditors and clients want to see.
What if we already have a DPO or privacy officer?
Then RealCob becomes their most important tool. The work is distributed across departments, the software compares the answers automatically, and your DPO steers from one dashboard.
How much time does it take our employees?
Very little. Everyone sees only the questions that match their own job, and smart question trees skip whatever does not apply. The organisation has a complete picture within 3 hours.
We are already ISO certified. Isn’t that enough?
No, that is a common misconception. ISO 27001 covers information security and only partly overlaps with the GDPR. The GDPR sets its own requirements — from the processing register to data subject rights — that you must arrange and be able to demonstrate separately. RealCob checks those obligations alongside your existing ISO setup.
Do we have to start over again next year?
No. You carry over answers and registers from the previous cycle and only process what changed. Every cycle gets faster than the one before.
Get it right once. Then you are done with it.
Try RealCob free for 30 days or book a 20-minute demo. You will see immediately what your organisation is missing, and how quickly it can be fixed.